Risk, control, audit-request, and evidence submission
For risk, control, audit-request, and evidence submission, define the required context, classification rules, and duplicate or missing-data checks before work enters the operating queue.
FREE CLAUDE & CODEX PLUGIN TEMPLATE
A real SOT-based GRC and Audit Management System PRD template connecting risk, control, audit-request, and evidence submission, control, risk, audit item, and remediation-status lookup, control testing, evidence review, issue assignment, and remediation handling, control coverage, audit issue, and remediation due-date reporting.
View source on GitHub · MIT licensed
USE CASE
Teams designing an internal operations system for business owner submitting controls and evidence and compliance and internal audit operations coordinator
CONTENTS
VIBESPEC VIEWER
Each screen is generated from the public SOT included with this template.
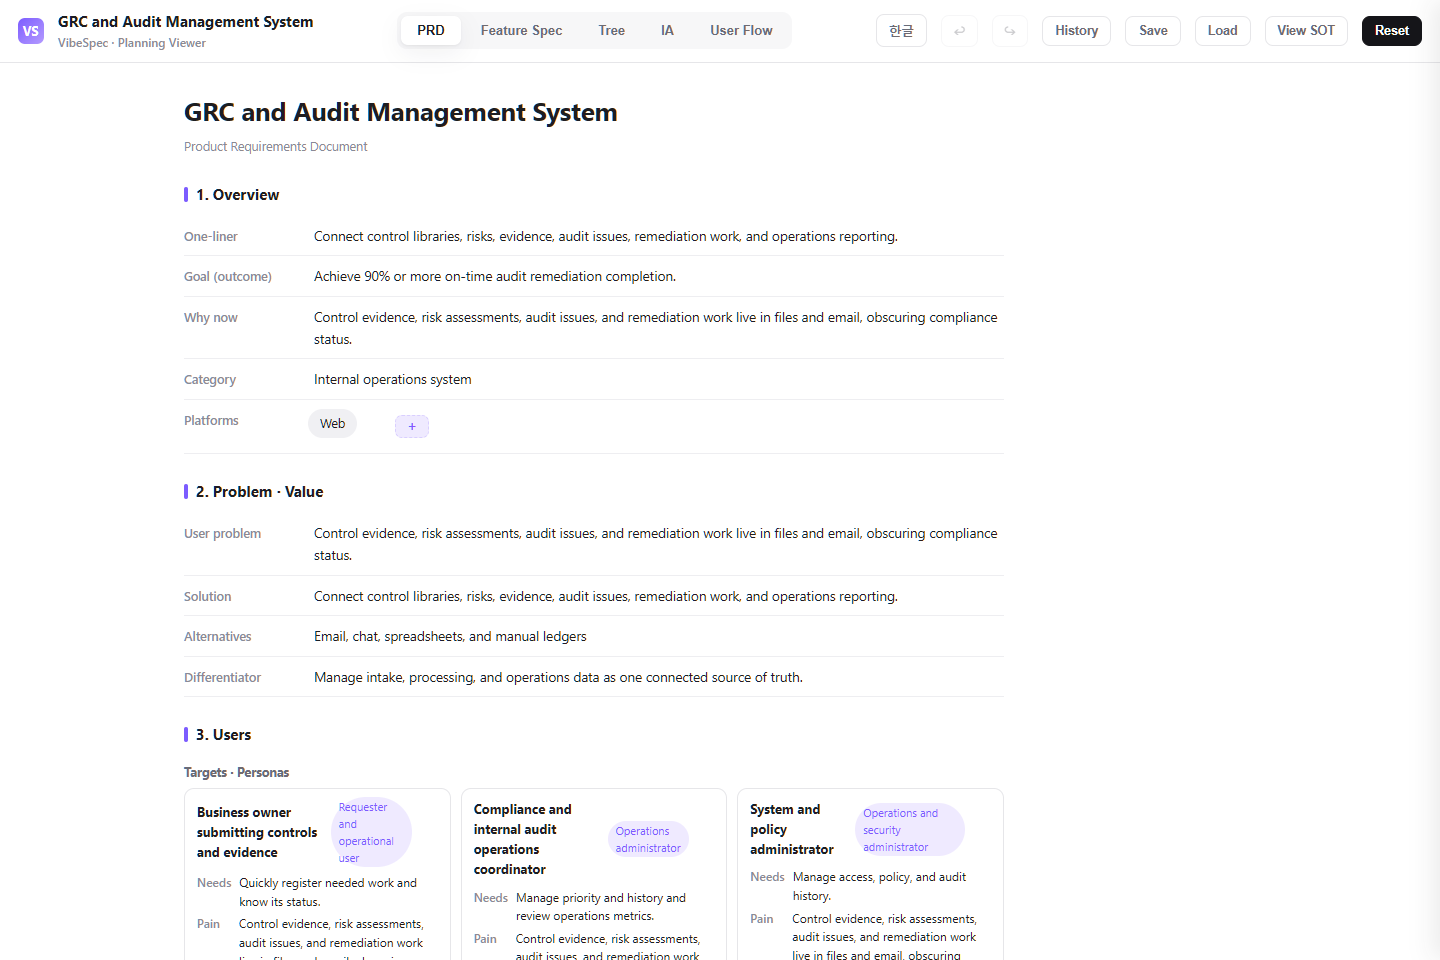 Open this screen in the live demo
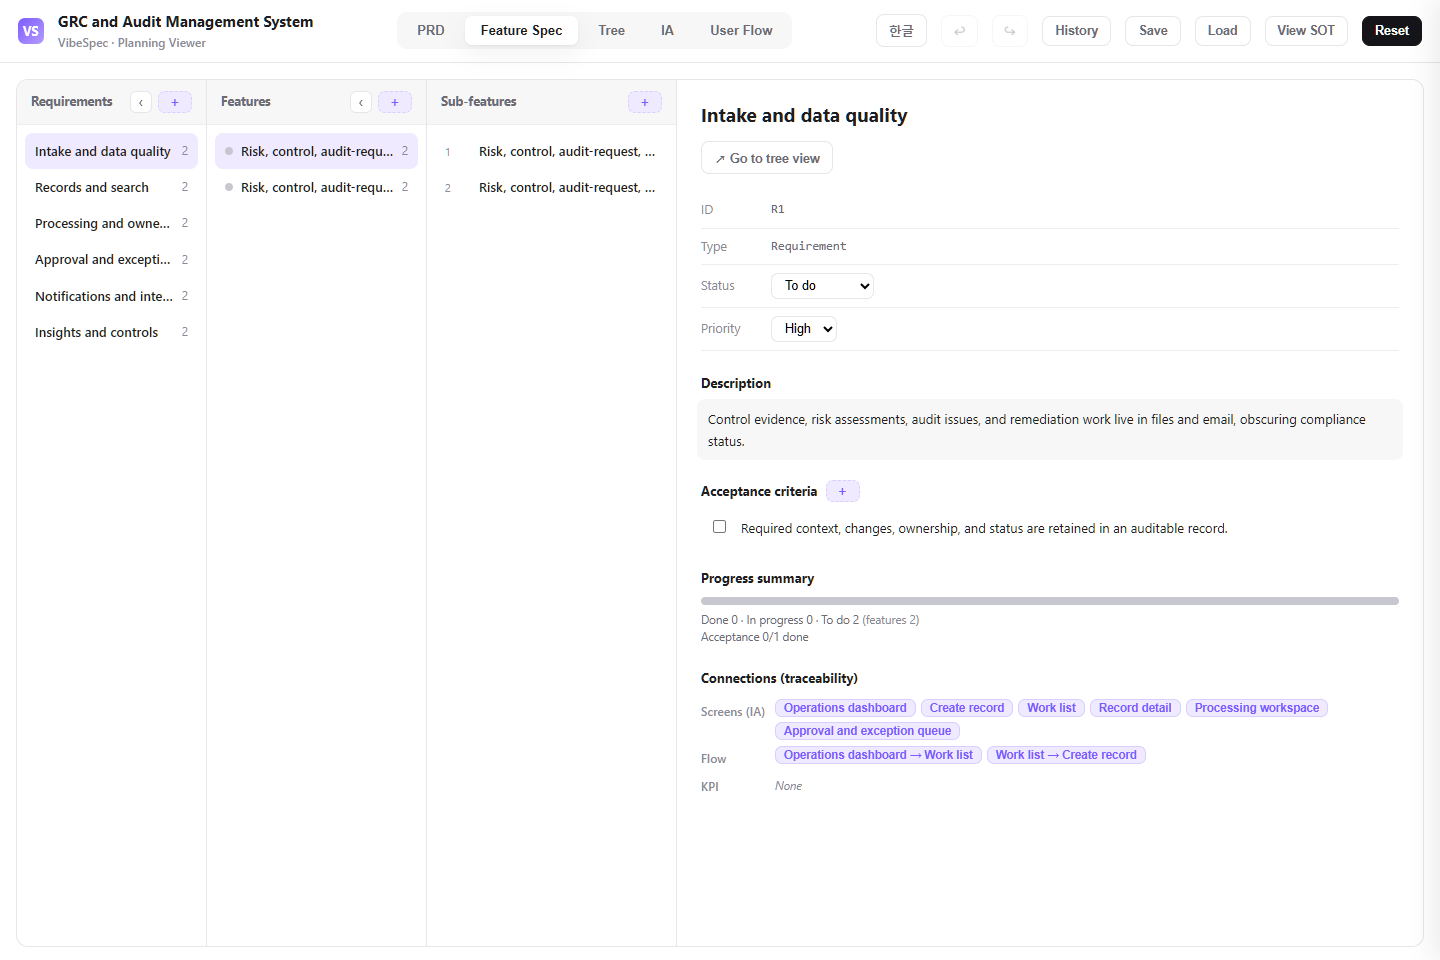 Open this screen in the live demo
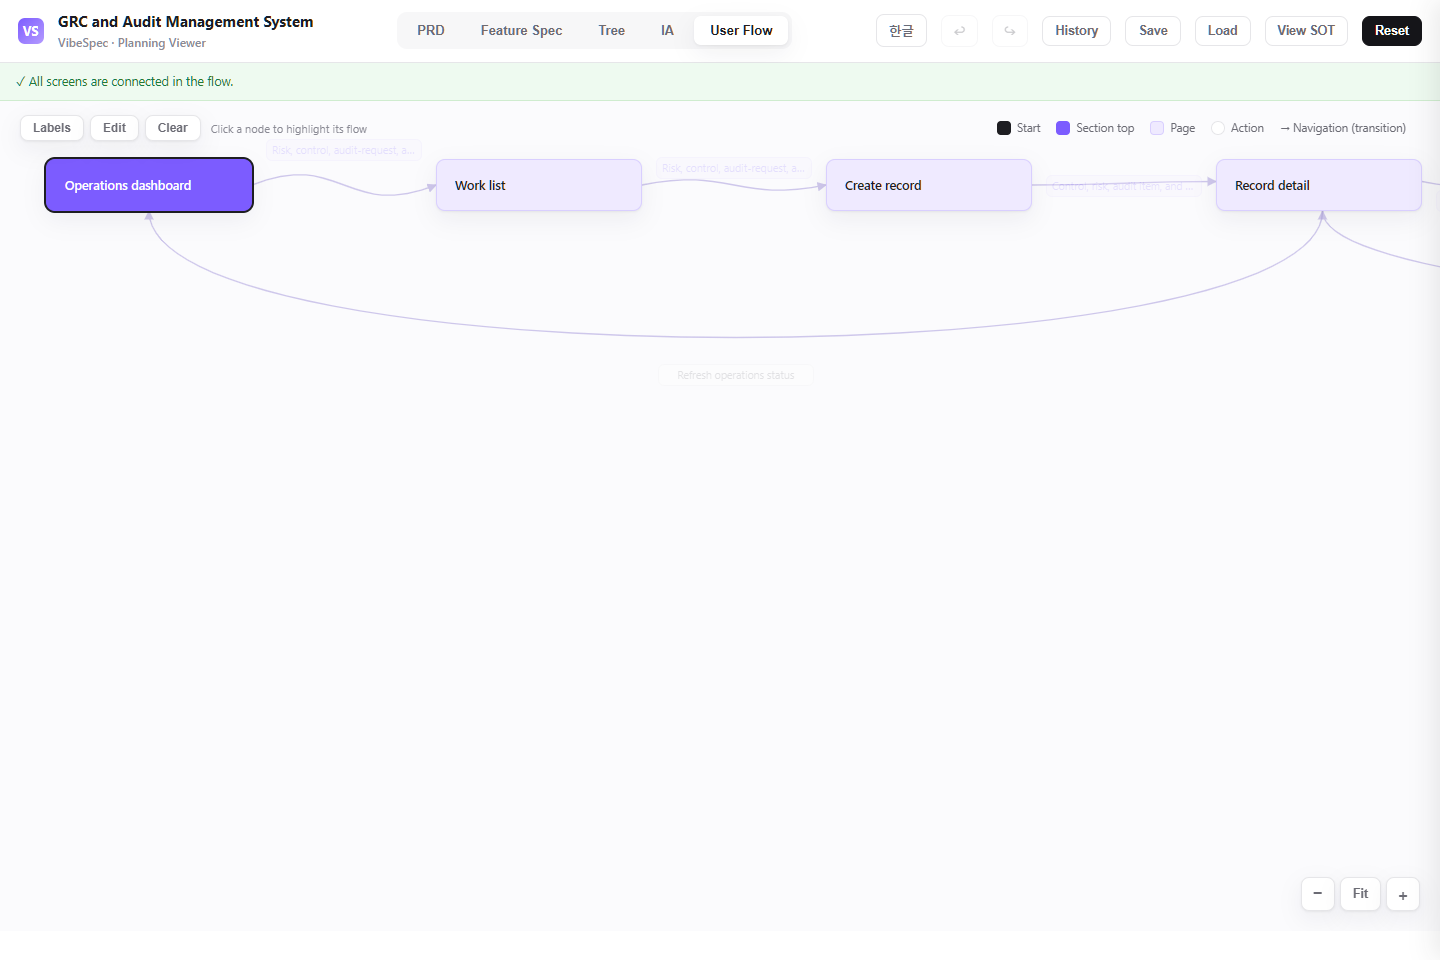 Open this screen in the live demo
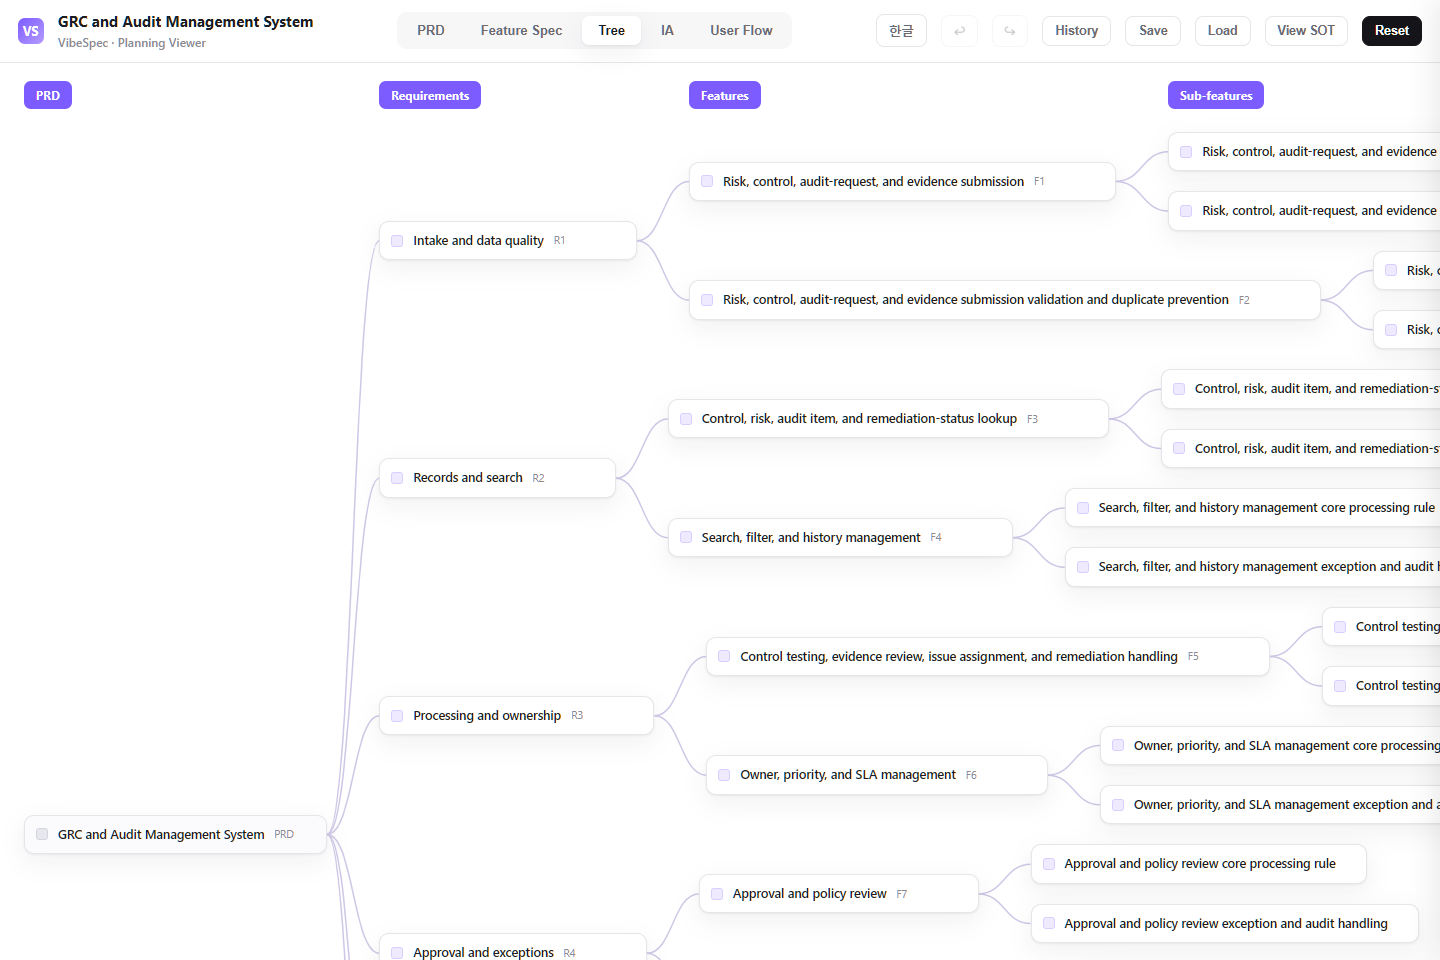 Open this screen in the live demo
PRACTICAL GUIDE
This GRC and Audit Management System connects risk, control, audit-request, and evidence submission, control, risk, audit item, and remediation-status lookup, control testing, evidence review, issue assignment, and remediation handling, and control coverage, audit issue, and remediation due-date reporting in one SOT-based planning document. Use the complete HTML to review and share the plan, then adapt the SOT JSON with the VibeSpec plugin in Claude or Codex.
For risk, control, audit-request, and evidence submission, define the required context, classification rules, and duplicate or missing-data checks before work enters the operating queue.
For control, risk, audit item, and remediation-status lookup, keep status, owner, priority, and change history together so the team can find the complete operating context.
In control testing, evidence review, issue assignment, and remediation handling, connect assignment, approval or rejection, exception handling, and completion confirmation as one accountable workflow.
Use control coverage, audit issue, and remediation due-date reporting to track due dates, bottlenecks, exceptions, and completion outcomes by team, period, and operating category.
Set the role-based access, audit history, notifications, and external-system boundaries that GRC and Audit Management System needs to operate safely.
The download opens in a browser without setup. Compare the PRD, feature specification, screen structure, and user flow with the work your team does today.
Write down real user roles, required data, approval rules, exceptions, and success metrics. Start with the core flow from risk, control, audit-request, and evidence submission through control testing, evidence review, issue assignment, and remediation handling.
Attach the SOT JSON in Claude or Codex with the VibeSpec plugin and describe the change in plain language. VibeSpec keeps requirements, features, screens, and user flows connected.
Replace the template vocabulary, states, and classification with the terms your team uses. Keep risk, control, audit-request, and evidence submission and control, risk, audit item, and remediation-status lookup consistent.
Define who registers, reviews, approves, processes, and confirms completion, plus the conditions that trigger rejection or reprocessing in control testing, evidence review, issue assignment, and remediation handling.
Decide what control coverage, audit issue, and remediation due-date reporting should measure, then connect any SSO, messaging, or adjacent-system integration to the related screens and user flow.
Create a separate GRC and Audit Management System initiative for due-date alerts, owner assignment, approval reminders, and exception follow-up.
Before connecting GRC and Audit Management System to source data or adjacent systems, define synchronization cadence, failure handling, access boundaries, and audit records.
Extend GRC and Audit Management System with team, period, and category analysis plus action rules for deteriorating completion or service levels.
Adapt this GRC and Audit Management System for our team. Ask about our user roles, states, required fields, and approval steps first, then update the requirements, screens, and user flows together.Reduce this GRC and Audit Management System to an MVP that keeps risk, control, audit-request, and evidence submission, control, risk, audit item, and remediation-status lookup, and control testing, evidence review, issue assignment, and remediation handling. Move automation and external integrations into separate initiatives.Create a separate initiative on top of this GRC and Audit Management System for due-date alerts and automatic owner assignment. Keep the connection to the existing screens and user flow.Yes. The complete HTML opens in a browser for review and sharing. To adapt the plan, attach the SOT JSON to Claude or Codex with the VibeSpec plugin and describe the change in plain language.
It includes risk, control, audit-request, and evidence submission, control, risk, audit item, and remediation-status lookup, control testing, evidence review, issue assignment, and remediation handling, and control coverage, audit issue, and remediation due-date reporting, plus foundations for access, audit history, notifications, and integrations.
The HTML is a complete planning document for reading and sharing. The SOT JSON is source data that VibeSpec can update while keeping requirements, features, screens, and user flows connected.
For a discrete capability such as automation, integration, or additional analytics, create and review a separate initiative before changing the product plan broadly.
WORKFLOW